
EU Regulations & Compliance
Operationalizing EU regulations into practice for IT departments.
How we deliver it
We take ownership of your information estate, knowing what you have, where it lives, and how it moves, so it's ready for regulators and the business alike.
- Current state & benchmark of your information landscape
- Map digital systems, interfaces & information assets
- Categorize and link assets to runtime storage and data flows
- Translate to a governed operating model
- Ongoing Strategy & Executive Reporting
- Lead Regulatory Advisor
- CSDM Architect
- Change & Adoption Lead
We scope every engagement to your team's current maturity, priorities and existing tools.
Scope this for your teamFrom regulatory requirements to operational reality
Regulation was too often treated as a checkbox. Now, in Europe, it's reshaping how critical organizations operate, not just how they report. Resilience, security and accountability are no longer audit footnotes; they're becoming part of the operating model itself.
Einar & Partners helps regulated organizations turn requirements such as DORA, NIS2 and the AI Act into ownership, governance, controls, reliable data and day-to-day operating practices.
Our footprint in EU regulations
Not just theory; we operationalize regulations at scale
Regulatory excellence starts with well-governed data and ownership. Many organizations are compliant but spend too much time gathering evidence and proving it. We help change that.
Where regulation meets IT Operations
Critical Functions (CIFs), including the mapping of underlying ICT Assets and Information Assets, ICT Risk Management, Incident Reporting, Resilience Testing, 3rd Party Management & Information Sharing.
Governance, risk ownership, critical assets, operational controls and resilience.
Ownership, risk classification, controls, accountability and operational governance for enterprise AI.
Beyond regulatory advisory: why organizations work with us
Access to the network
Executive roundtables, peer cohorts and independent forums with organizations facing similar regulatory challenges.
Proprietary regulatory intelligence
Benchmarks on maturity, internal effort, budgets and implementation progress across European organizations.
Proven blueprints
Reusable governance, ownership, asset and service-model patterns shaped through real regulatory programmes.
From regulation to implementation
We translate requirements into controls, ownership, data, evidence and operating practices, then implement them with internal teams.
Our Delivery: From baseline to operational compliance
During the pilot, we apply our framework to measure internal effort, cost and capacity required to scale, giving leadership a quantified view before committing to broader rollout.
Research & Publications
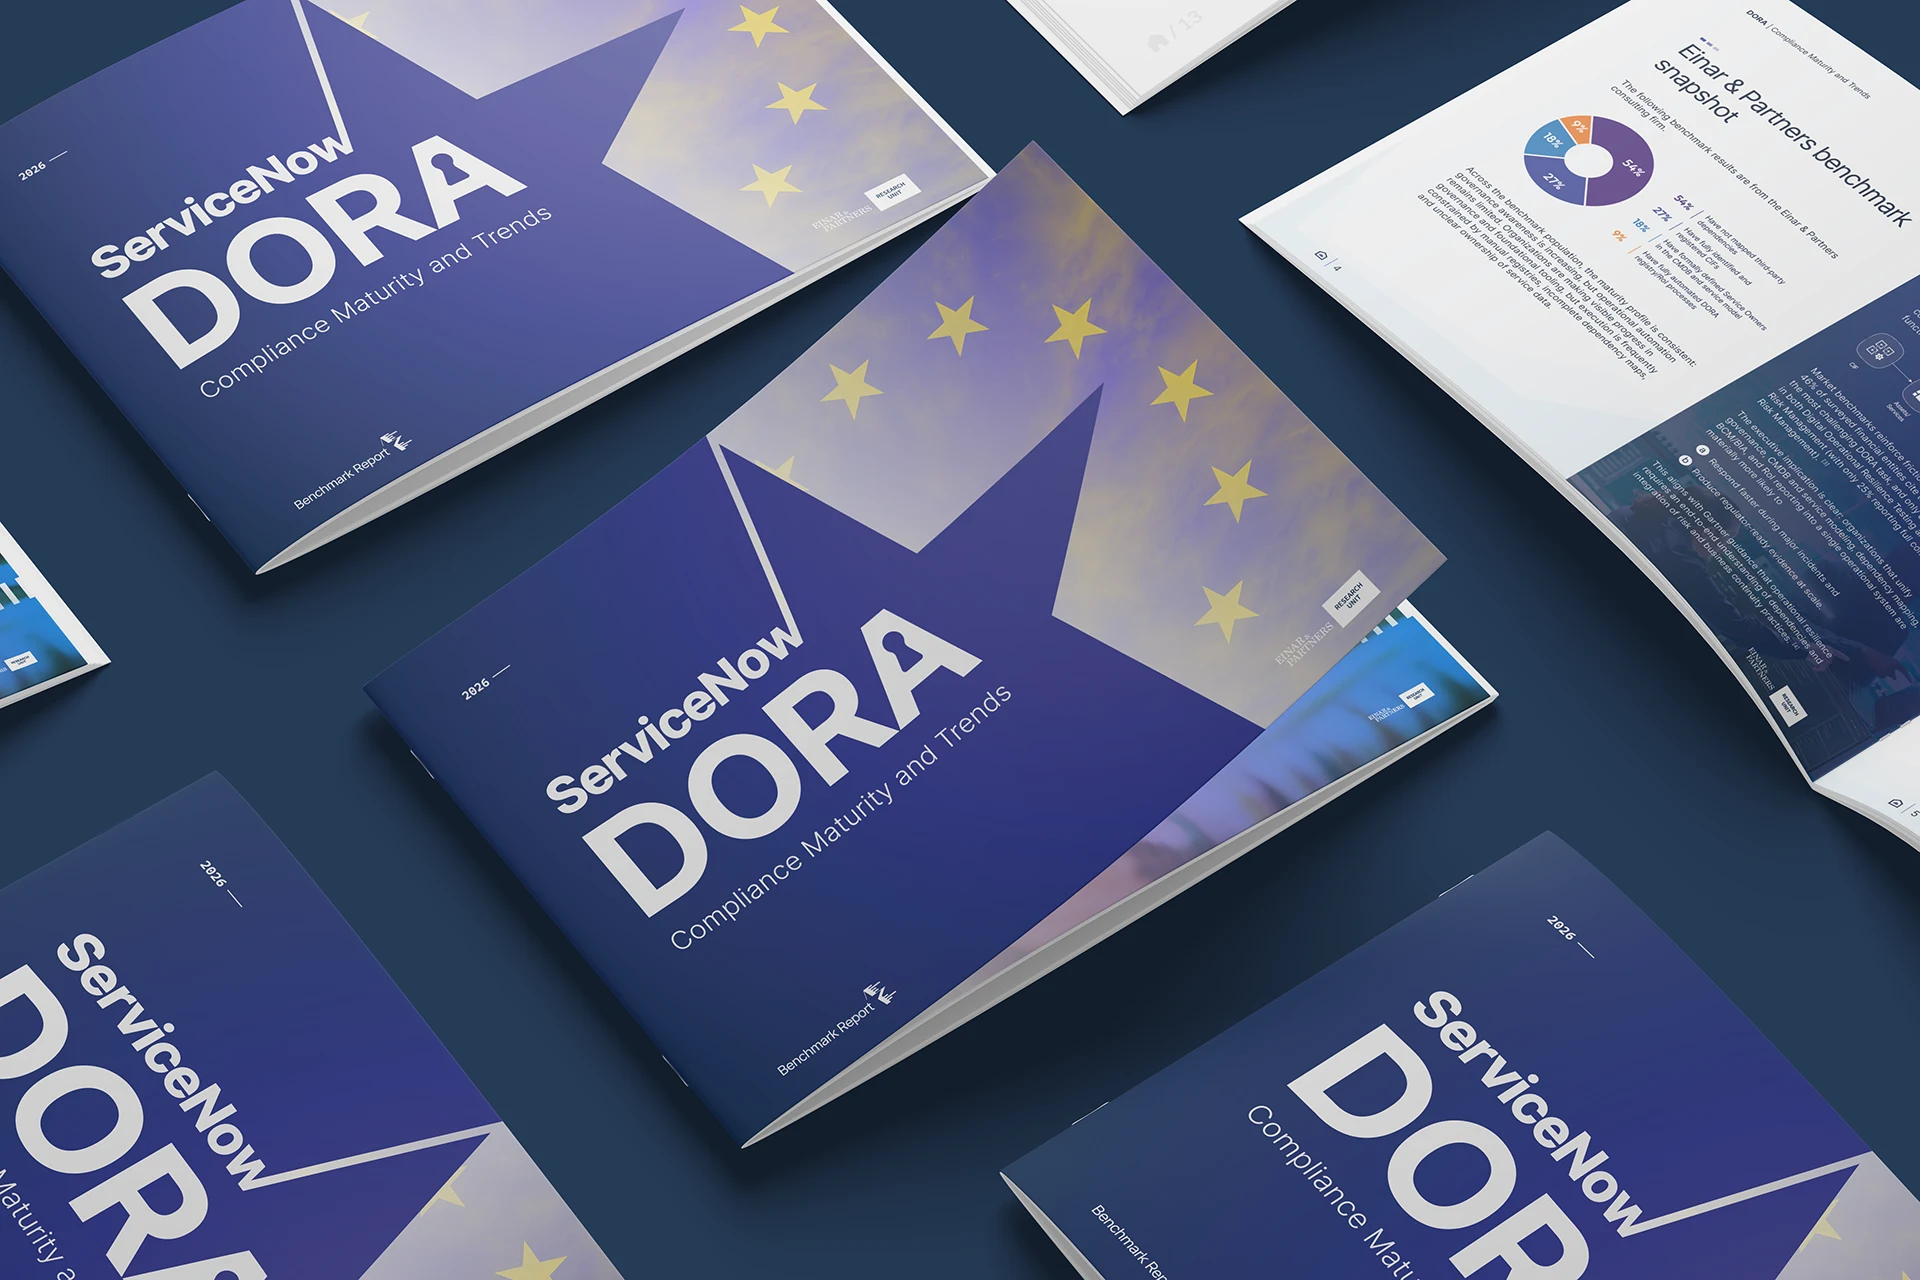 Report
DORA Maturity Index
Benchmark your organization's DORA maturity against European peers.
Explore Now
NIS2 CSDM
A closer look at NIS2 through the Common Service Data Model, with ServiceNow.
Explore NowUnderstand where your organization stands.
Benchmark your regulatory readiness and identify the gaps that matter operationally.